PRACTICAL GUIDE: How to Build a Corporate Policy for AI Governance and Management
PREMISE
The adoption of artificial intelligence in a company represents a strategic opportunity, but it requires a structured approach to ensure security, regulatory compliance, and maximization of benefits. This document provides practical guidelines for building an effective corporate policy on AI governance.
1. WHY A CORPORATE AI POLICY IS NEEDED
The Problem: Shadow AI
The "Shadow AI" phenomenon occurs when employees use unauthorized artificial intelligence tools (such as public ChatGPT, Claude, Gemini) without the approval or knowledge of the IT department or management.
Significant data:
17% of large companies have banned unapproved AI tools 77% of companies fear AI hallucinations 74% are unable to scale AI value 0% traceability of uncontrolled AI decisions
Concrete Risks of Shadow AI
Privacy and Security Risks:
- Sensitive company data shared with external providers
- No control over where data goes and how it is used
- Possible use of data for training third-party models
- Violation of corporate data protection policies
Compliance and Regulatory Risks:
- GDPR violation due to improper handling of personal data
- Non-compliance with the European AI Act (in force since February 2, 2025)
- Lack of mandatory human oversight
- Significant legal risks and penalties of up to 6% of global turnover
Operational Risks:
- IT has no visibility into which AI tools are being used
- No traceability of decisions made
- No control over the quality of responses
- Impossibility of conducting audits
- Hidden and uncontrolled costs
2. APPLICABLE REGULATORY FRAMEWORK
Applicable European and Italian Regulations
AI Act (EU Regulation 2024/1689):
- Mandatory training of personnel (from February 2, 2025)
- Classification of AI systems by risk level
- Mandatory human oversight for high-risk AI
- Complete documentation and traceability
- Conformity assessment for critical systems
GDPR (EU Regulation 2016/679):
- Data minimization and privacy by design
- Right to be forgotten and data portability
- Data Protection Impact Assessment (DPIA) for AI
- Informed consent for personal data processing
- Data residency in Europe
ISO/IEC certifications in progress:
- ISO 42001 - AI Management System
- ISO 27001 - Information Security
- ISO 9001 - Quality Management
3. STRUCTURE OF THE CORPORATE AI POLICY
3.1 GENERAL PRINCIPLES
Human-centricity:
AI assists people, it does not replace them. Final control always remains human. Focus on augmented intelligence, not total automation.
Transparency:
Every use of AI must be declared and traceable. Clear documentation of how AI systems work. Transparent communication to stakeholders.
Privacy by Design:
Data protection from the design stage. Minimization of data collection. End-to-end encryption and security.
Human Oversight:
Human control at every critical stage. Ability to override AI decisions. Validation of outputs before use in production.
Regulatory Compliance:
Full compliance with GDPR, the AI Act, and sector-specific regulations. Continuous updates as legislation evolves. Periodic compliance audits.
3.2 ORGANIZATIONAL GOVERNANCE
Structure of the AI Committee
Establish an AI Governance Committee composed of:
- AI Officer / Chief AI Officer - Strategic lead for AI implementation
- IT/CTO - Infrastructure management and technical security
- Legal/Compliance - Regulatory compliance and legal risks
- HR - Training and change management
- Business Units Representatives - Representatives from various departments
- Data Protection Officer (DPO) - Privacy and GDPR compliance
Responsibilities and Duties
- Definition of the corporate AI strategy
- Approval of use cases and pilot projects
- Monitoring KPIs and performance
- Budget and priority management
- Periodic reviews (monthly/quarterly)
- Management of AI-related incidents
3.3 AUTHORIZED AND PROHIBITED TOOLS
APPROVED TOOLS
Centralized Corporate Platform:
Define a single authorized platform for the use of AI within the company.
Characteristics of the approved platform:
- Centralized access management
- Complete traceability of interactions
- Integrated human oversight
- Multi-LLM (no vendor lock-in)
- Flexible deployment (Cloud, Private Cloud, On-Premise)
- Guaranteed GDPR and AI Act compliance
PROHIBITED TOOLS
Unauthorized Consumer Tools:
- Public ChatGPT, Claude, Gemini for sensitive corporate data
- Any AI not approved by IT
- Services that do not guarantee zero data retention
- Providers that do not respect European data residency
Basic rule: Data classified as Confidential or Secret may be used ONLY on the approved corporate platform.
3.4 DATA CLASSIFICATION AND MANAGEMENT
| Level | Description | Permitted AI Use |
|---|---|---|
| Public | Data already public or intended for publication | Any tool (with caution) |
| Internal | Non-sensitive information for internal use | Preferred corporate platform |
| Confidential | Commercial, financial, strategic data | ONLY corporate platform |
| Secret | IP, patents, personal data, critical information | ONLY on-premise/private platform |
AI Data Governance Rules
- Data Minimization: Share only strictly necessary data
- Data Residency: Preference for solutions with data hosted in Europe
- Zero Data Retention: Providers must not retain data
- Audit Trail: Complete log of who accesses which data
- Right to be Forgotten: Ability to delete data upon request
3.5 MANDATORY TRAINING
Training Paths by Level
General Awareness (Whole company - 2 hours):
- What generative AI is and how it works
- Opportunities and risks
- Corporate policy and authorized tools
- Practical examples and use cases
AI Academy Basic (Managers and Power Users - 4/5 days):
- Fundamentals of Generative AI and Large Language Models
- Creation and management of AI Agents
- Effective prompt engineering
- Integration into corporate workflows
- AI Act and GDPR compliance
Advanced Training (IT and Developers - 3-5 days):
- Enterprise integrations (CRM, ERP, API)
- Secure authentication (SSO, OAuth, JWT)
- MCP Server and advanced functions
- Security best practices and deployment
- Monitoring and troubleshooting
Important note: As of February 2, 2025, the AI Act makes training mandatory for personnel using AI systems.
3.6 ACCESS CONTROL AND PERMISSIONS
RBAC Model (Role-Based Access Control)
Access Levels:
- Viewer - Only consultation of public agents
- User - Use of agents authorized for their role
- Creator - Creation and modification of agents for their team
- Admin - Full management of agents and users in the department
- Super Admin - Total platform control (IT/AI Officer)
3.7 TRACEABILITY AND AUDIT
Mandatory Logging
Every interaction with AI must be tracked:
- Timestamp of the interaction
- User who made the query
- AI agent used
- Input provided and output generated
- Any manual modifications
- Human oversight applied
3.8 HUMAN OVERSIGHT
Basic Principle: No critical decision can be made exclusively by AI without human validation.
| Risk | Use Case Examples | Oversight |
|---|---|---|
| Low | Documentation research, email drafts | User review |
| Medium | Quotes, customer responses | Approval workflow |
| High | HR decisions, financial analysis | Co-creation |
| Critical | Medical decisions, safety | Human veto |
4. AI ADOPTION PATH IN 4 PHASES
PHASE 1: TRAINING (1-2 months)
Objective: Make the team autonomous and aware
Deliverable: Trained team, approved policy, first AI agents created
PHASE 2: CLOUD PoC (2-3 months)
Objective: Validate the value of AI with real cases
Use Case: Knowledge Management, Customer Support, Onboarding, Sales
Deliverable: Documented ROI, feasibility report
PHASE 3: MODEL STUDY (1 month)
Objective: Define final deployment strategy
Analysis: Workload, TCO, Compliance, Vendor Selection
PHASE 4: PRODUCTION (gradual scaling)
Objective: Bring AI to enterprise scale
Options: On-Premise (enterprise) or Private Cloud
On-Premise Advantages: Full control, maximum privacy, 180% Hyper-depreciation
5. AI GOVERNANCE PLATFORM
Essential Features
Centralized Control
RBAC with granular permissions, SSO user management, team segmentation, instant access revocation
Total Traceability
Complete audit log of conversations, decision tracking, agent history, export for compliance
Flexible Multi-LLM
Zero vendor lock-in, support for GPT-4/Claude/Mistral/Gemini, local models, cost optimization
Automatic Compliance
AI Act and GDPR compliant, EU data residency, zero data retention, ISO certifications
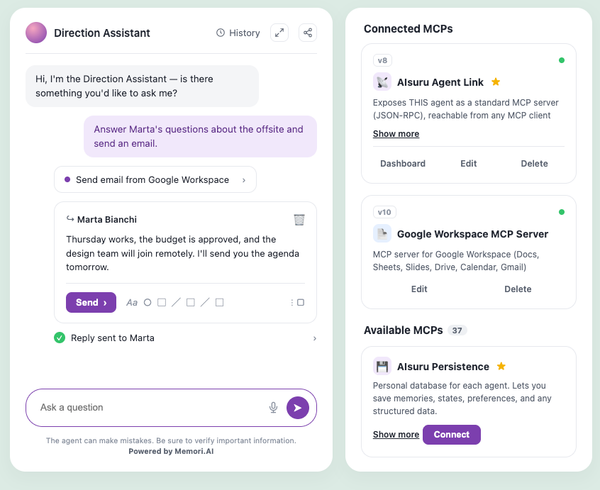
The Solution: AIsuru by Memori.ai
AIsuru is the Italian platform that meets every corporate AI governance need.
Key advantages:
- Full IT control: Centralized dashboard, total visibility
- Flexible deployment: SaaS, PaaS, Private Cloud, On-Premise
- Guaranteed compliance: Italian, GDPR and AI Act compliant
- Certified training: AIsuru AI Academy with TD SYNNEX
- Multi-LLM: No lock-in, instant provider switching
- Integration-ready: MCP Server, REST API, CRM/ERP
6. INVESTMENT AND TAX OPPORTUNITIES
2026 Hyper-depreciation (Law 199/2025)
Exceptional Opportunity
Hyper-depreciation allows you to increase by 180% the tax-deductible cost of the investment for goods compliant with Industry 4.0.
Applicable Annexes:
- Annex IV (Hardware): AI servers, GPUs, edge computing, storage
- Annex V (Software): AI platforms, LLMs, Agentic AI software
Practical Example
On-Premise Investment: €150,000
- Hardware (Annex IV): €100,000
- AIsuru Software (Annex V): €50,000
With 180% Hyper-depreciation:
- Higher tax deduction: €150,000 × 1.8 = €270,000
- Tax savings (IRES 24%): €270,000 × 24% = €64,800
- Actual net cost: €85,200 (€150,000 - €64,800)
Validity: January 1, 2026 → September 30, 2028
7. IMPLEMENTATION CHECKLIST
Governance and Organization
- AI Governance Committee established
- Corporate AI Officer appointed
- AI policy written and approved
- Policy communicated to the whole company
Regulatory and Compliance
- GDPR and AI Act compliance assessed
- DPIA completed
- Supplier contracts verified
- External audits scheduled
Tools and Technology
- Centralized AI platform selected
- Deployment decision made (Cloud/Private/On-Premise)
- SSO/Active Directory integration
- Active monitoring and alerting
Training
- Training plan defined
- General awareness delivered
- AI Academy completed
- Certifications issued
Operations
- Pilot use cases identified
- First AI agents created
- KPIs and dashboard configured
- Incident management procedure active
8. CONCLUSIONS AND NEXT STEPS
Why Act Now
- Regulatory Obligation: AI Act requires training since February 2, 2025
- Competitive Advantage: Companies with governed AI win
- Tax Opportunity: 180% Hyper-depreciation until September 2028
- Shadow AI Risk: Without governance, the company is exposed
- Market Pressure: Customers demand guarantees on AI use
Final Recommendations
- Do NOT improvise: AI without governance is a risk
- Start with training: The foundation for any success
- Choose compliant platforms: Avoid consumer tools
- Think scalable: PoC with a production vision
- Document everything: Traceability is fundamental
Confindustria Support
Memori.ai has signed an agreement with Confindustria Emilia Centro to support member companies.
Available Services:
- Consulting for building an AI policy
- Free process assessment
- Certified training via AIsuru AI Academy
- Subsidized PoCs to validate ROI
- Support for the 2026 Hyper-depreciation
- On-premise deployment with certified partners
📞 CONTACTS AND RESOURCES
For further information and support:
Memori srl
Email: demo@memori.ai
Phone: (+39) 051 19470234
Website: www.memori.ai
Training
AIsuru AI Academy:
www.memori.ai/it/ai-academy
Course registration:
academy.tdsynnex.com
Documentation:
docs.aisuru.com
Partnerships
- TD SYNNEX - Distribution and training
- Lenovo + NVIDIA - On-premise hardware
- Confindustria Emilia Centro - Agreement for member companies
Document by Memori srl
January 2026 - Version 1.0
This document is provided for informational purposes. For advice specific to your company's situation, contact Memori's experts or your trusted legal/tax advisor.